IP Allowlist is available on all plans except for the free plan.
IP Allowlist can be used to restrict which IP addresses are permitted to access your database by comparing a connection's address with predefined CIDR blocks. This feature enhances database security by allowing connections only from specified IP addresses. For example if you have dedicated production servers with static IP addresses, enabling IP allowlist blocks connections from other addresses.
Enabling IP Allowlist#
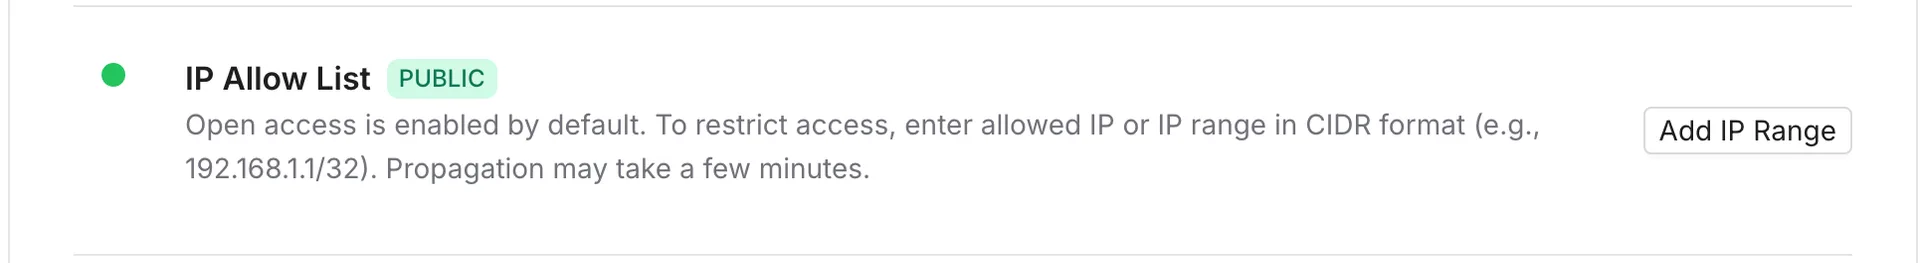
By default, any IP address can be used to connect to your database. To enable the allowlist:
- Open the database you want to protect in the Upstash Console.
- Go to the
Configurationsection on the database details page. - Add at least one IP range to the allowlist. The allowlist becomes active once the first range is saved.
- Add more ranges to allow additional clients. Meeting the criteria of just one range is enough to establish a connection.
You can either provide
- IPv4 address, e.g.
37.237.15.43 - CIDR block, e.g.
181.49.172.0/24
Currently, IP Allowlist only supports IPv4 addresses.
It may take a few minutes for changes to propagate.
What Happens to Blocked Requests#
Once the allowlist is enabled, the database compares each connection's address with the predefined CIDR blocks. Connections from addresses that match none of the listed ranges are rejected, so clients on those addresses cannot reach the database.
Serverless Environments#
IP Allowlist only works when your clients connect from static, known IP addresses. On serverless platforms such as AWS Lambda and Vercel Functions the egress IP is not under your control, so allowlisting is usually not possible there. As an alternative, consider VPC Peering or Private Link to restrict access from your own infrastructure, or contact us for Enterprise options.